Select Language

Choose your language

株式会社ヤグラ

Select Language

Choose your language

株式会社ヤグラ

Select Language

Choose your language

Yagura AI SOC

24/7 Alert Monitoring

AI SOC Agent

AI SOC Agent
Monitoring Alerts
24/7/365

24/7 Alert Monitoring

AI SOC Agent

Maximize the ROI of Your EDR and SIEM

Maximize the ROI of Your EDR and SIEM

Yagura AI SOC is a security operations service that uses AI to investigate EDR and SIEM alerts and support response decisions.

Yagura AI SOC is a security operations service that uses AI to investigate EDR and SIEM alerts and support response decisions.

Service icon
Service icon
Service icon
Service icon
Service icon
Service icon
Service icon
Service icon
Service icon
Center icon
🛡️Detect Danger
🛡️Detect Danger
🛡️Detect Danger
🛡️Detect Danger
🛡️False positive
🛡️False positive
🛡️False positive
🛡️False positive
🛡️False positive
Service icon
Service icon
Service icon
Service icon
Service icon
Service icon
Service icon
Service icon
Service icon
Center icon
🛡️Detect Danger
🛡️Detect Danger
🛡️Detect Danger
🛡️Detect Danger
🛡️False positive
🛡️False positive
🛡️False positive
🛡️False positive
🛡️False positive

Scroll

CHALLENGES

CHALLENGES

Traditional SOCs cannot keep pace in the generative AI era.

Why you need the AISOC Agent

Issue 01

Missed detection risks from high alert volume and false positives

Traditional SOCs are hitting their limits, relying on brute-force human effort to handle the endless alerts generated by SIEMs and other tools.
Issue 02

Analyst dependency and delayed response

Security incident investigation and assessment rely heavily on the experience and skills of individual analysts, resulting in a lack of speed.
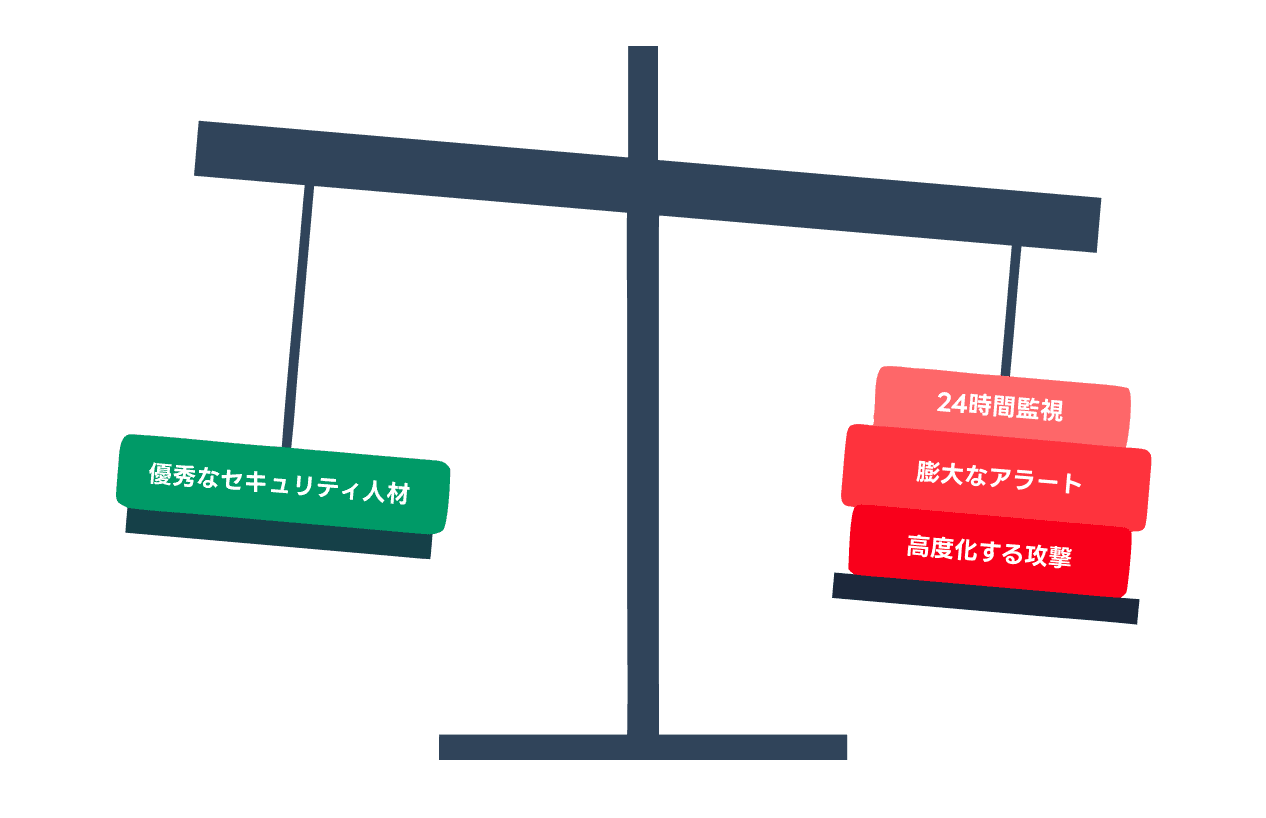
Issue 03

Severe Shortage of Cybersecurity Talent

With intense competition for advanced analytical talent, building and maintaining an in-house 24/7 monitoring operation is extremely difficult.

SOLUTION

SOLUTION

How Yagura AI SOC, the AI SOC Agent, Works

SOLUTION 01

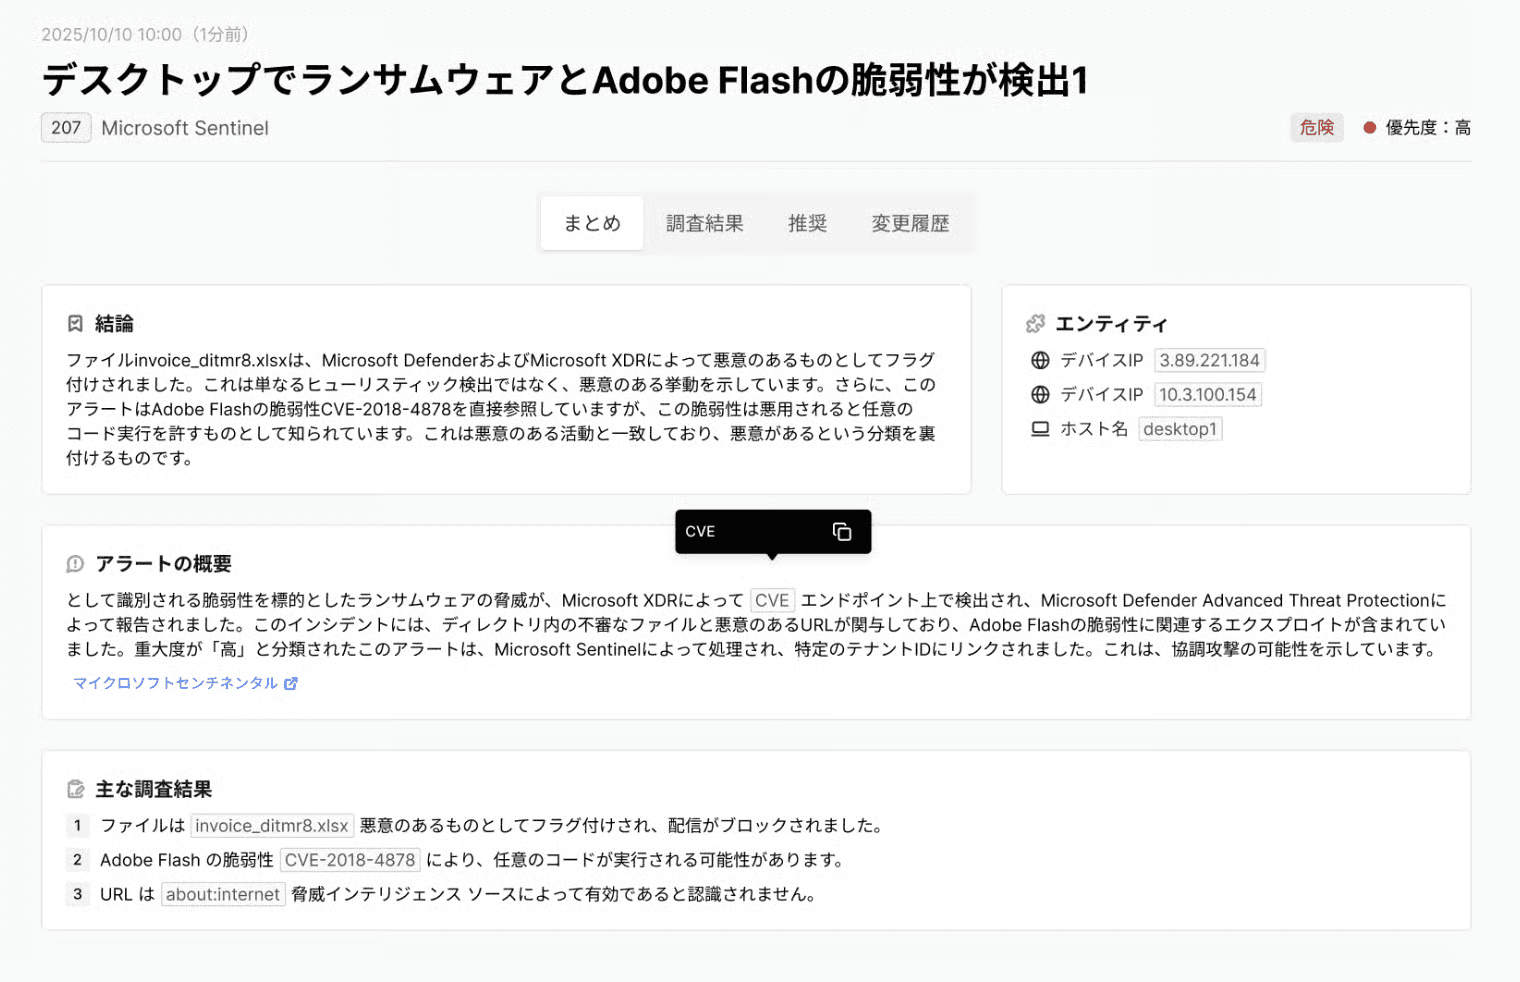
Autonomous Security Alert Investigation Powered by AI

Relying solely on manual analysis to investigate the massive volume of alerts generated daily by SIEM and other security products is no longer sustainable. Organizations need a system that can accurately identify critical threats buried beneath false positives.

Autonomous Investigation

Authenticity Verification

Rapid Resolution
SOLUTION 02

Improving AI Investigation Accuracy
with Context Memory

AI learns your organization's specific knowledge (Wikis, past incident history, and ticket management systems). This enables optimal investigation and decision-making tailored to your organization, moving beyond generic advice.

Knowledge Learning

Contextual Understanding

High-Accuracy Detection

SOLUTION 03

Integrates with 100+ EDR, SIEM,

and Identity Products

Seamlessly integrates via API with over 100 security products, including major EDR, SIEM, and IdP solutions. Build an advanced, automated monitoring system instantly while leveraging your existing environment.

API Integration

Leverage Existing Infrastructure

Instant Deployment

Service icon
Service icon
Service icon
Service icon
Service icon
Service icon
Service icon
Service icon
Service icon
Center icon
🛡️Detect Danger
🛡️Detect Danger
🛡️Detect Danger
🛡️Detect Danger
🛡️False positive
🛡️False positive
🛡️False positive
🛡️False positive
🛡️False positive
Service icon
Service icon
Service icon
Service icon
Service icon
Service icon
Service icon
Service icon
Service icon
Center icon
🛡️Detect Danger
🛡️Detect Danger
🛡️Detect Danger
🛡️Detect Danger
🛡️False positive
🛡️False positive
🛡️False positive
🛡️False positive
🛡️False positive

EVALUATION

EVALUATION

Measure AI SOC outcomes under consistent conditions

In a case involving a major newspaper company, investigation time fell from 2 hours 30 minutes to 2 minutes. Verify results in your own environment through a PoC with consistent scope, period, and measurement start and end points.

Evaluation metric

MTTR
(Mean Time to Recovery)

Recovery time

Investigation completion rate

Manual analysis time

Human resources

What to measure

What to measure

From detection to recovery

Scoped / completed alerts

Work time per alert

Total hours during the period

Measurement notes

Mean and median

Include uninvestigated alerts

Compare under the same conditions

Include review effort

CASE STUDY

CASE STUDY

Security Awareness Training Case Study

A multi-channel training example using Yagura Awareness
We felt the need for "advanced AI-driven defense" to counter "advanced AI-driven attacks."

In recent years, attackers have expanded their tactics beyond email phishing to more sophisticated social engineering methods. Recognizing this trend, we introduced the system to further elevate employee crisis awareness by conducting multi-faceted training that covers not only email phishing, but also smishing and vishing.

Finance

CISO

Dear Mr. Kunihiko Sato

Yagura AI Security

Service Overview

Download for Free

Explore the changing cybersecurity landscape

and get an overview of Yagura’s services.

Yagura AI Security

Service Overview

Download for Free

Explore the changing cybersecurity landscape
and get an overview of Yagura’s services.

Yagura AI Security

Service Overview

Download for Free

Explore the changing cybersecurity landscape
and get an overview of Yagura’s services.