



Scroll




CHALLENGES
CHALLENGES
Ransomware and Targeted Attacks: Beyond the Limits of Manual Monitoring
Once inside, attackers lie dormant for long periods while escalating their privileges. With the continuous expansion of monitored environments—including UTM, EDR, and cloud services—manually analyzing logs is no longer feasible. Relying on post-incident detection is too late to prevent damage.
Issue 01
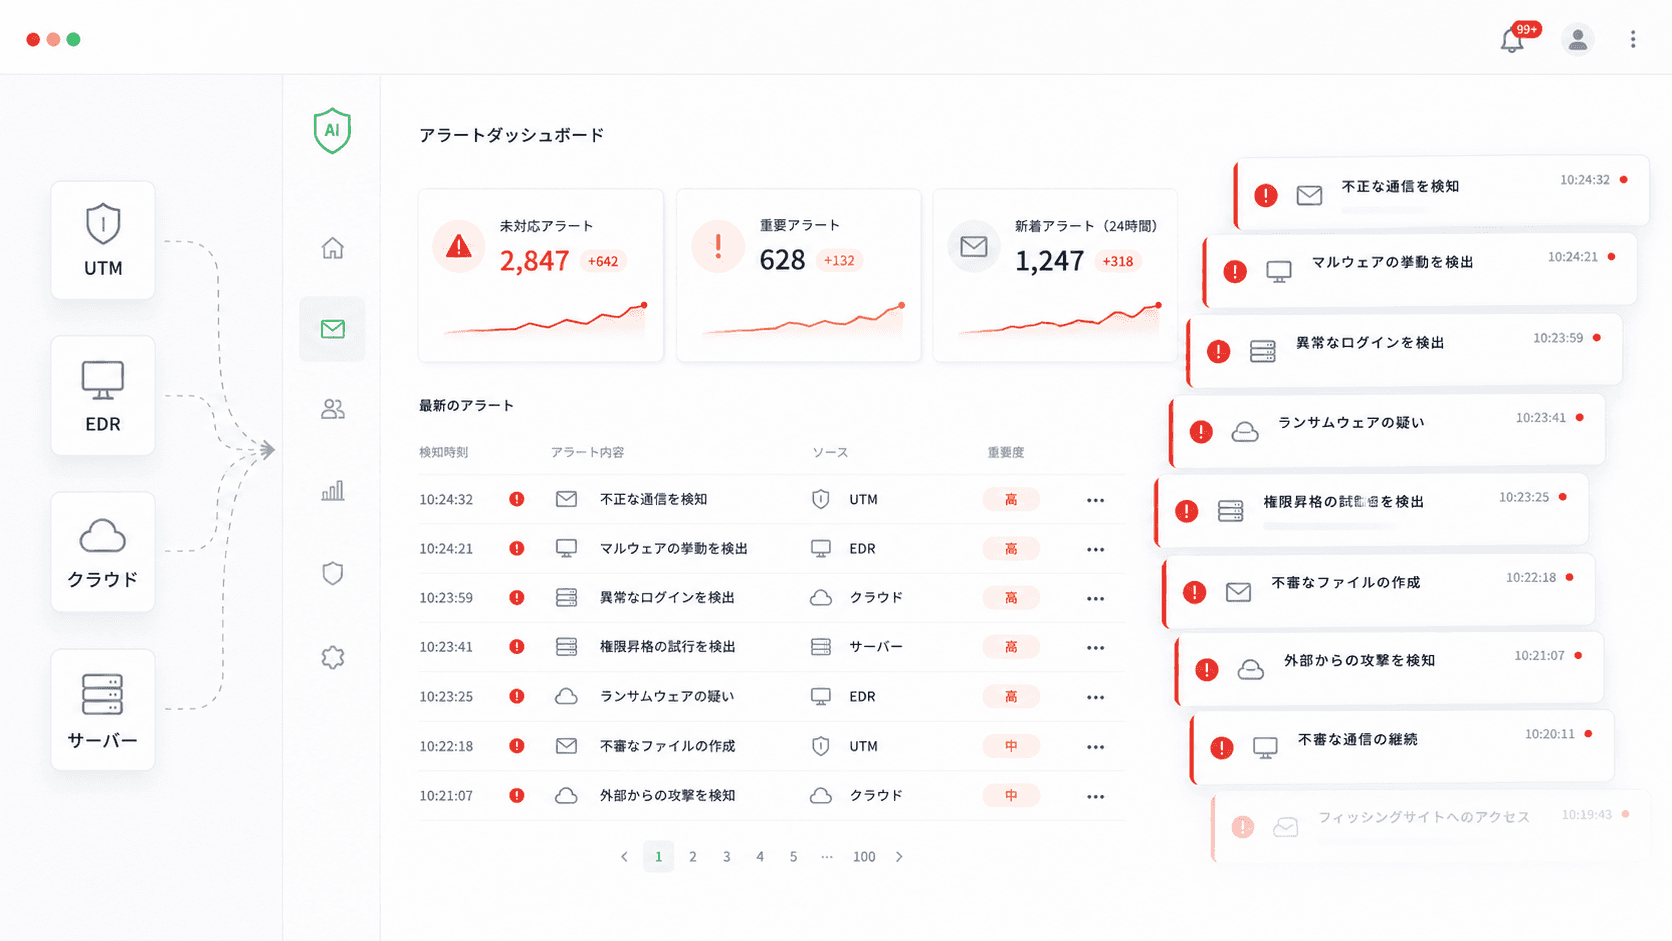
Manual monitoring cannot keep pace with the ever-increasing volume of logs.
While the number of logs to manage—from UTM, EDR, to cloud—continues to increase, keeping dedicated security personnel on site at all times is impractical.
The situation is worsening as massive log volumes lead to missed detections that are only noticed after the fact.

Issue 02
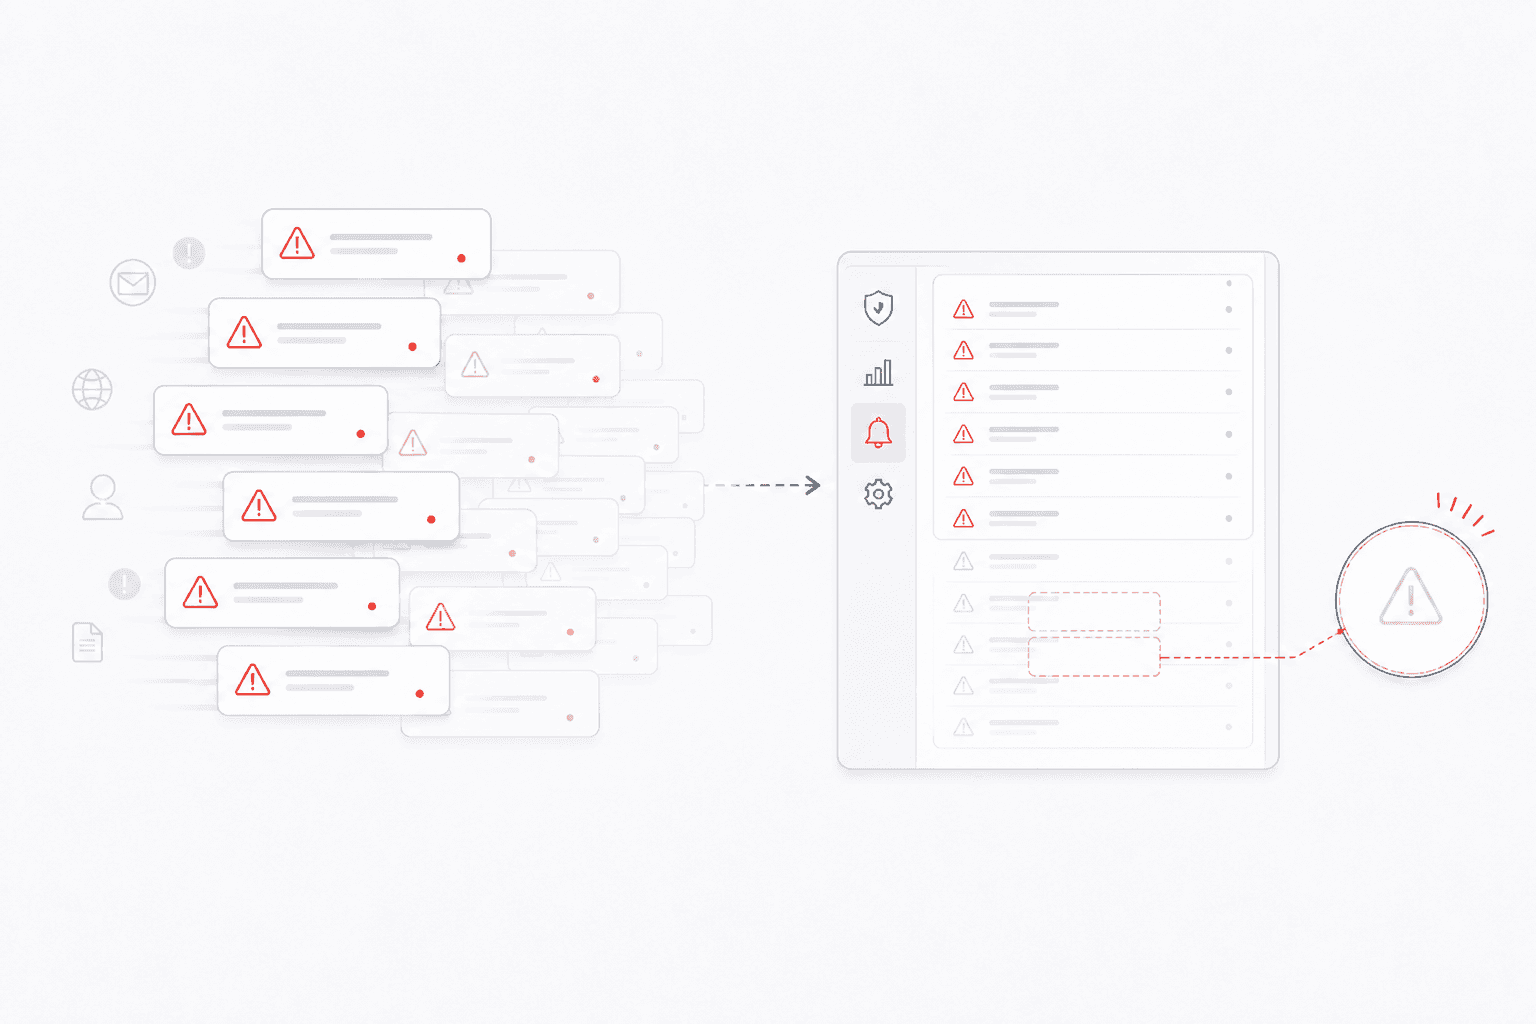
Buried in a flood of alerts, missing the real threats
Rule-based SIEMs generate high rates of false positives. Reacting to endless alerts delays response to true high-risk incidents, burying critical threats.
Issue 03
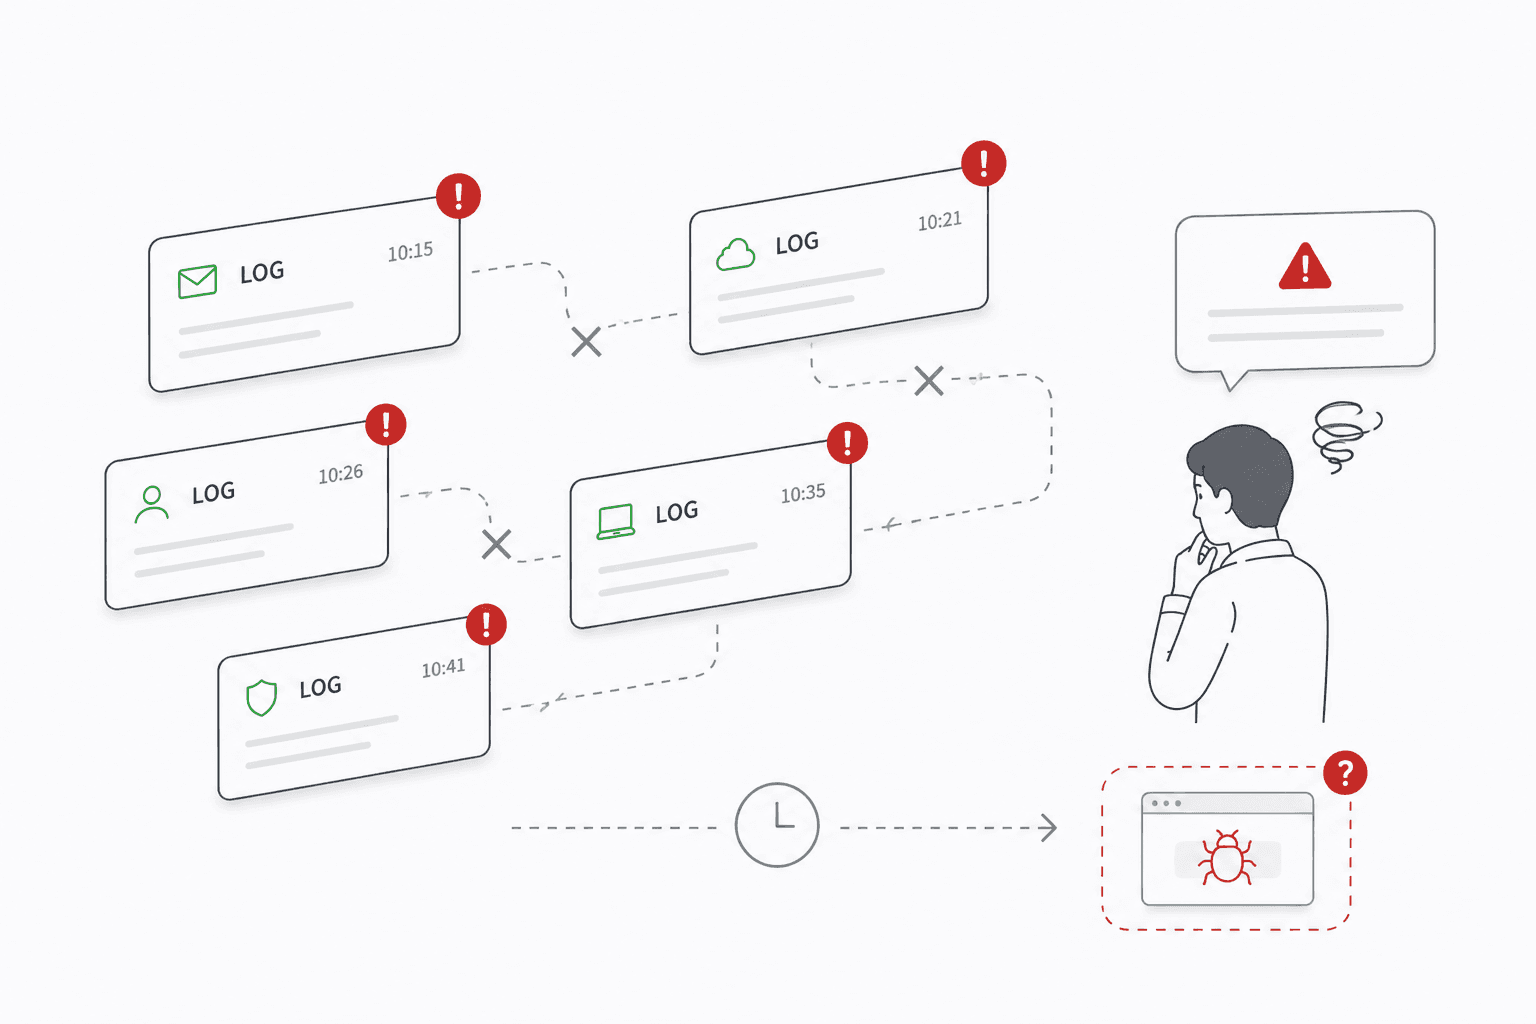
Unable to grasp the full scope of the attack, delaying containment
When logs from each product are siloed, a single log cannot reveal the full picture of an attack. If you cannot immediately identify who breached your system, when, and where, the damage will continue to spread.
SOLUTION
SOLUTION
How Yagura AI SIEM Works
SOLUTION 01
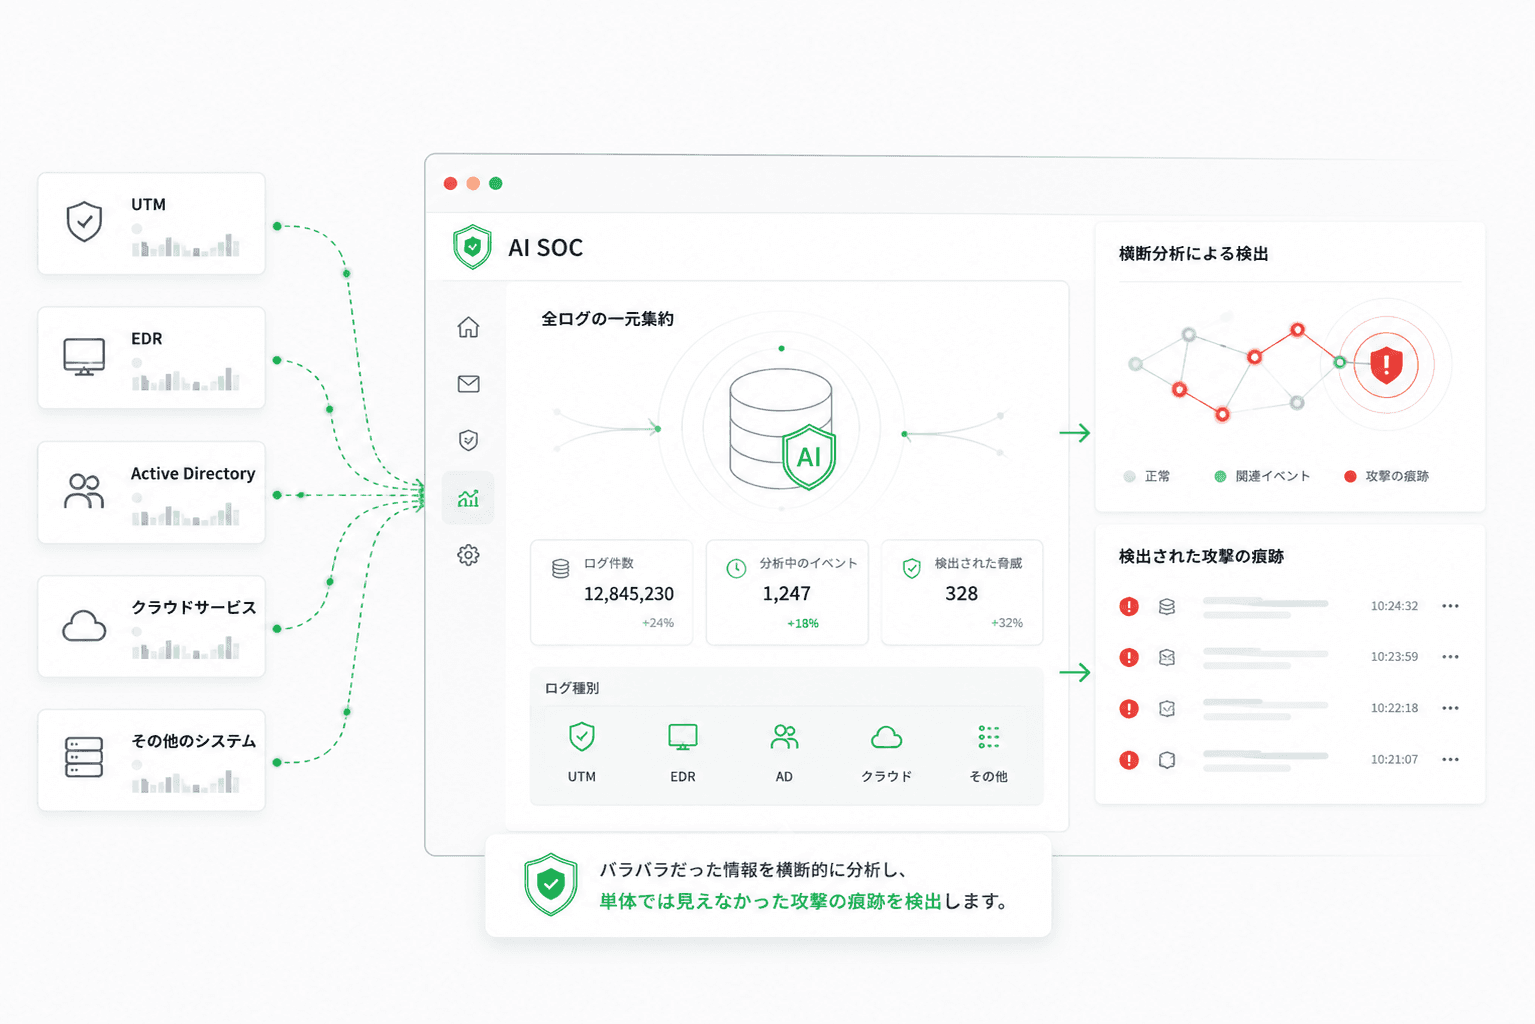
Centralized Log Aggregation and Cross-Analysis
Consolidate logs from UTM, EDR, Active Directory, and cloud services into AI SIEM to support cross-sectional analysis. Correlate multiple logs to investigate signs of attack and the scope of impact. Collection targets and integration methods will be confirmed during deployment.
EDR Integration
UTM Integration
Cloud Compatible
SOLUTION 02
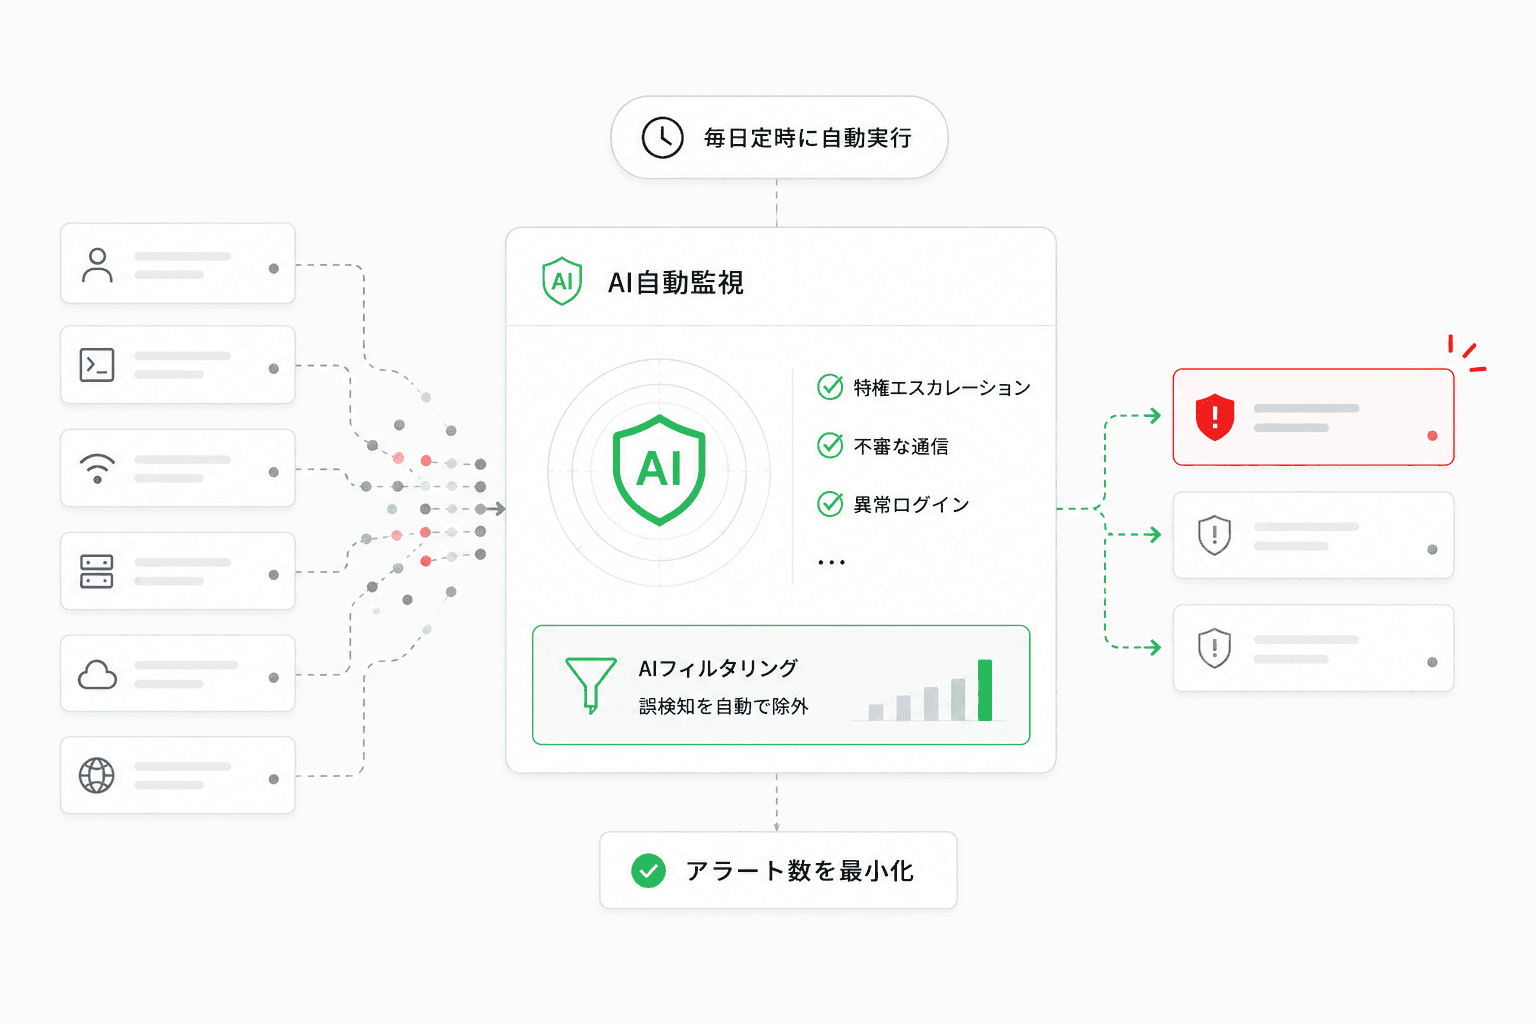
AI-Driven Threat Hunting and Automated Monitoring
AI analyzes collected logs to investigate signs of permission changes, suspicious communications, and anomalous logins. It organizes relevant logs and priorities, helping personnel review and make response decisions.
AI-Powered Automated Monitoring
Reduce false positives
Threat Hunting
SOLUTION 03
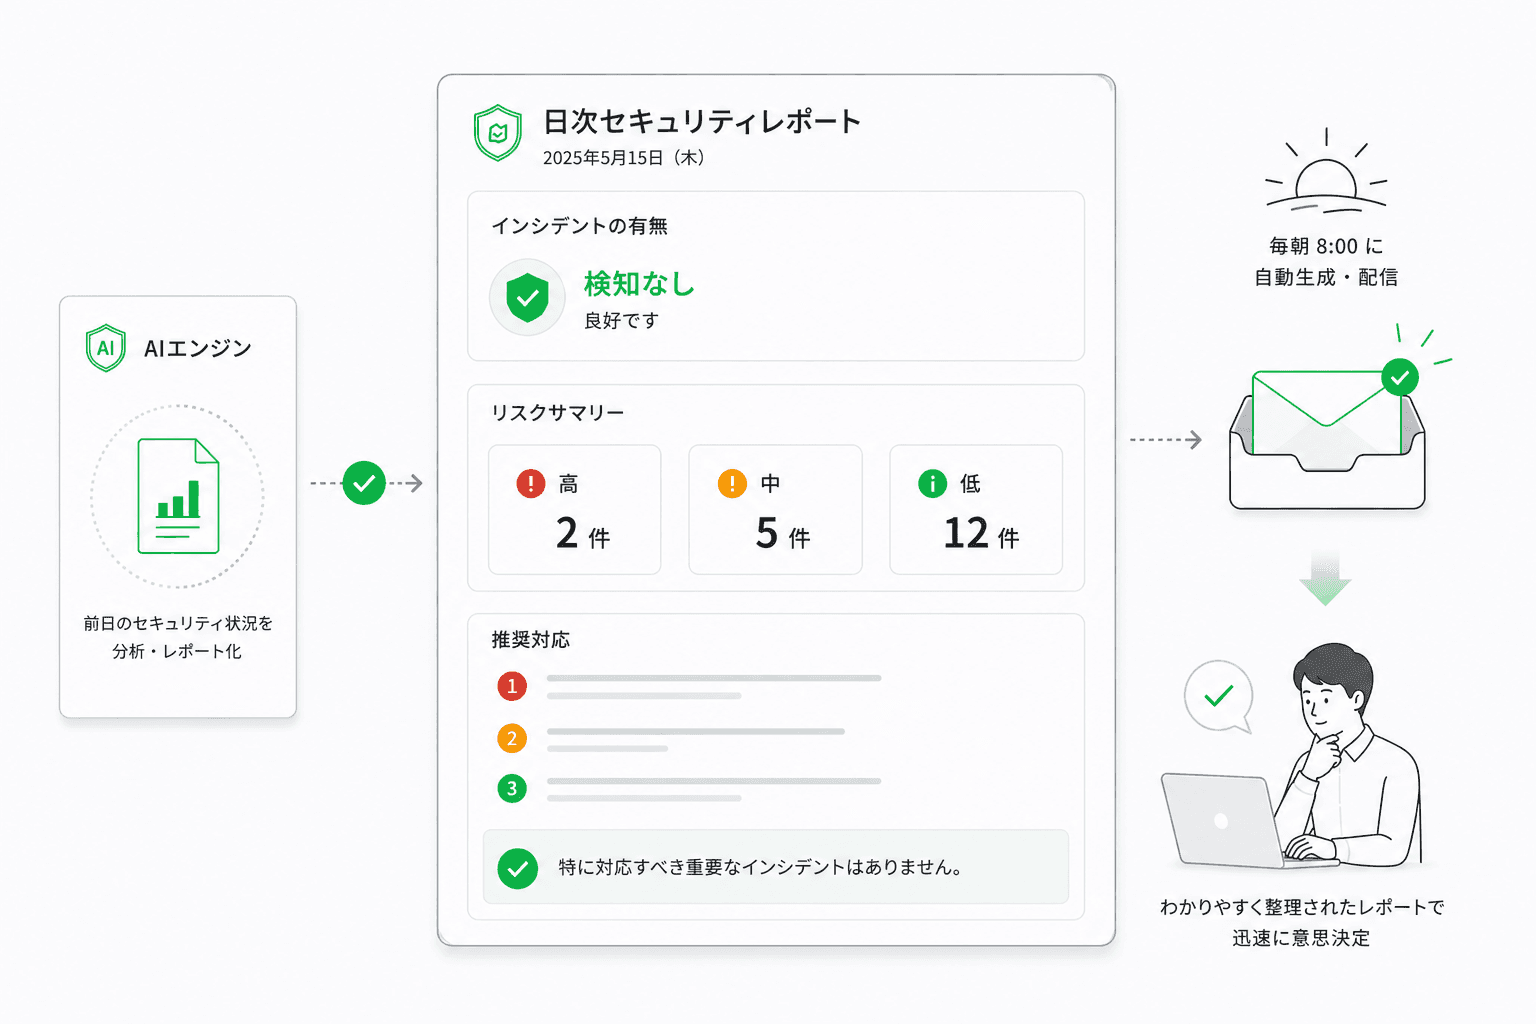
Automated Daily Security Reports
Every morning, AI automatically generates a report of the previous day's security status. It clearly organizes incident presence, priority, and recommended actions, enabling rapid decision-making even without a dedicated specialist.
AI Report Generation
Prioritization
Executive Dashboard
BENEFIT
BENEFIT
Yagura AI SIEM: Supporting Log Analysis and Situational Awareness
From log aggregation to threat investigation and reporting
Detection Method
False Positive Management
Required Expertise
Rule-based
Manual sorting
Advanced SOC Analyst Required

AI-Powered Automated Monitoring
AI Automated Filtering
No Dedicated Administrator Required
CASE STUDY
CASE STUDY
Yagura Awareness Case Studies

